open source OWASP aligned

Guardrails scan text. Agents take actions. SHAI governs what they do.

SHAI was built to help secure autonomous agents. It’s a security harness that sits between your agent and its tools, scanning every boundary, gating every tool call, enforcing policy, and producing a tamper-evident audit trail.
It’s open source, works with any agent or framework, and is designed against the OWASP Agentic AI Top 10.

Why SHAI exists

Agents are not chatbots anymore. They are execution systems.


Agents don't just answer questions anymore. They write code, send emails, deploy infrastructure, move money. Every connected tool gives the agent more capabilities and expands the blast radius. Unlike a traditional app, nothing bounds that scope except the model's own reasoning about what to do next.

LLMs are becoming increasingly powerful, and that power carries real risk, precisely because we’re giving them autonomy and access to systems we haven’t fully secured to begin with.

SHAI is the security harness that wraps around an agent. It makes sure the surrounding system is engineered the way any high-privilege caller should have been engineered from day one.
The deterministic checks are written in plain code rather than left to another model’s opinion, and they sit between the proposal and the action.

The Secure harness

The harness around the agent loop.


SHAI started as a security research project on autonomous agents. Agents are running on systems that we have not fully secured yet, and securing those systems will take years. We wanted a way to let agents work safely now.


Works with the frameworks people already use

Nothing to rebuild. SHAI ships with integrations for
LangGraph LangChain CrewAI Anthropic SDK PydanticAI OpenAI Agents

An existing agent can pick SHAI up without rewriting the loop logic. Each framework runs its own loop and dispatches tools its own way. Implementing it takes four awaited calls per turn:

Python
verdict = await harness.scan_input(user_text, ctx)
gate    = await harness.check_tool_call(tool_name, args, ctx)
verdict = await harness.scan_tool_result(result, ctx)
verdict = await harness.scan_output(response, ctx)

SHAI places a deterministic check at each of those transitions, before the LLM reads the input, before the tool runs, after the tool returns, and before the response reaches the user. Each check emits one signed audit event.

The architecture
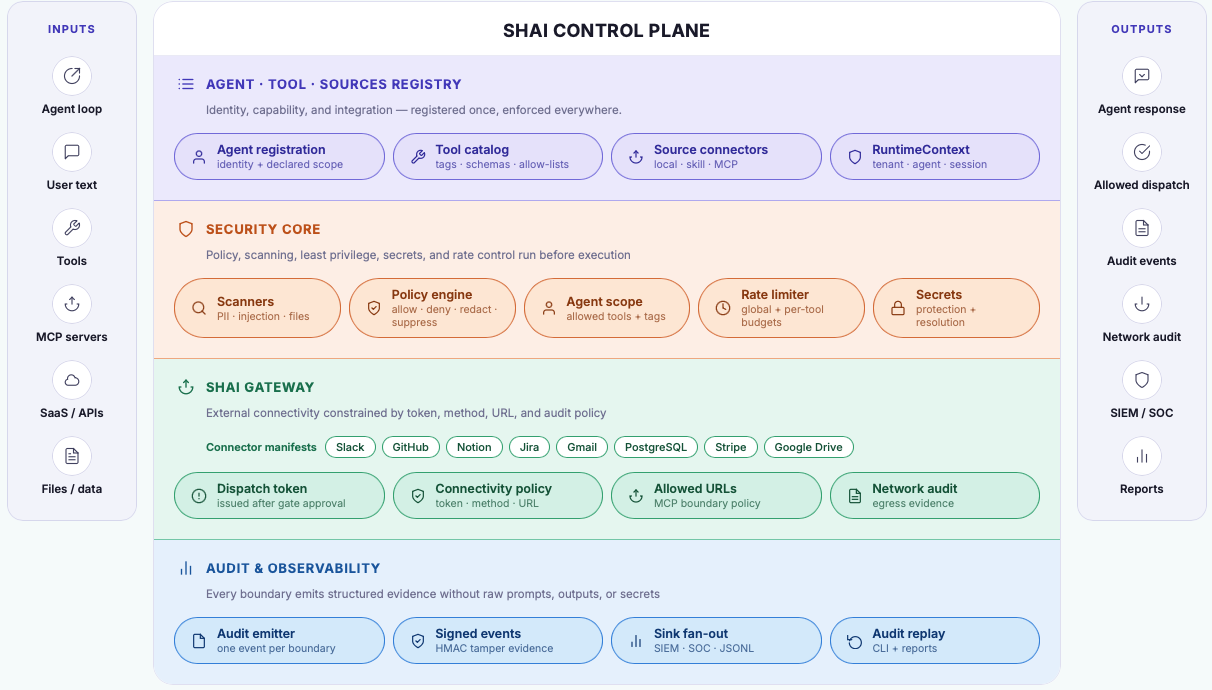
Agent turn flowing through five SHAI boundaries: input scan, tool gate, tool result scan, output scan, and the signed audit event stream.

Differentiation

How SHAI is different from LLM guardrails

An autonomous agent is a thinking system with tools, one that reads emails, documents, browses the web, executes code, calls APIs, stores memories, spawns sub-agents, and makes decisions on its own.

An autonomous agent's security surface spans several distinct problems, including hostile user input, a malicious file upload, a tool call the LLM shouldn't make, a tool result carrying instructions the LLM will treat as authoritative, and a session drifting adversarially over multiple turns.

A malicious webpage or phishing email can hand it instructions disguised as content. The agent stores those instructions in memory and acts on them three sessions later. This is an example of Memory Poisoning, one of the OWASP Agentic AI Threats.

LLM guardrails such as Guardrails AI, NeMo, LlamaFirewall, Rebuff, and Lakera validate LLM inputs and outputs. They classify text, which is useful and complementary to SHAI, but they do not gate tool calls, scan tool results, enforce per-agent capability scoping, or emit a signed audit trail.

SHAI treats the whole agent lifecycle as the unit of enforcement, not just the text going in and out of the model.

SHAI runs a seven-layer, deterministic tool-call gate between the LLM proposing a tool call and the tool running, covering the allowed-tool set, argument rules, irreversibility, subagent capability scope, policy intersection, cross-boundary signal correlation, and optional argument scanning. Code decides,not the model's own judgement. It supports the principle of "Least Agency": grant an agent only the autonomy a bounded task needs.

Get started

Wire SHAI into an existing agent in minutes.


Pick a template. Add SHAI to the loop. The agent stays as it is, while the boundaries wrap around the tool calls.

The docs ship as a set of skills that can be queried interactively for anything the templates don't cover.

Security controls

Every control is executable code, mapped to a concrete threat.

Most of what SHAI enforces lines up with the OWASP Top 10 for Agentic Applications, published by the OWASP GenAI Security Project. But not limited to it.

Part 1

OWASP Agentic Top 10 (2026)

ASI01 · Agent Goal Hijack

Partial

Every entry point is scanned before content reaches the LLM.

Injection, jailbreak, and identity-spoof catalogs run at the user input, file, and tool-result boundaries, each merged with its French, Spanish, German, and Mandarin variants. A cross-turn accumulator catches escalation spread across turns that each stay under the per-turn threshold.

ASI02 · Tool Misuse and Exploitation

Full

Seven-layer gate on every tool call, no exceptions.

Operator's config draws that line action by action, so one agent can be cleared to read a customer record and refused the ability to change it. Every LLM-proposed tool call goes through the gate, which checks it against the list of allowed actions. Deterministic, not heuristic.

ASI03 · Identity & Privilege Abuse

Partial

A subagent holds at most what its parent granted.

This is the most consistently reported failure in enterprise agent deployments: shared API keys, inherited user sessions, overpermissioned service accounts, and an agent that can reach systems its function never needed. Tools and capability tags must be a subset of the parent's, refused at load if they aren't, and re-checked by the gate on every call. Only agents registered with SHAI can call tools. Credentials stay behind secret:// URIs, resolved at load and never written into config.

ASI04 · Agentic Supply Chain Vulnerabilities

Partial

An MCP source is built only when its manifest hash matches an approved baseline.

The GitHub MCP exploit and the Amazon Q compromise, which reached a coding assistant with more than 950,000 installs, both arrived through something the agent depended on rather than something a user typed. The baseline is re-checked when the source connects and again on every tool call, so an edited manifest is refused at both. Tool names, descriptions, and tags come from the approved manifest rather than the remote server's own listing, and are scanned for injected instructions. Pattern updates are HMAC-signed and verified row by row before they apply.

ASI05 · Unexpected Code Execution

Limited

Dangerous command composition is caught at any boundary.

A code-execution agent carries the maximum exposure here. A command can be written to look like ordinary text. It arrives in a message someone types, a file they upload, or the reply a tool sends back. Hand it to the system and it executes with every permission the agent holds. SHAI checks each of those, plus the arguments the agent passes to a tool and the text it sends back out. Sandboxing what already runs belongs to your runtime.

ASI06 · Memory & Context Poisoning

Partial

Everything that reaches memory has crossed a SHAI boundary.

Anything an agent reads is potentially adversarial, including its own memory, so a poisoned document or retrieval record can shape a decision several runs after it lands. A webpage the agent browses or an email it reads can carry instructions dressed as ordinary content. So user input, uploads, and retrieval results are all scanned before the LLM ingests them. Anything the agent then writes to memory is itself a tool call, so it passes the gate like any other action.

ASI07 · Insecure Inter-Agent Communication

Out of scope

SHAI governs the boundaries around a single agent. The channel between two agents sits outside it.

It has no transport of its own between agents and does not authenticate peers. Compose with a message layer that does.

ASI08 · Cascading Failures

Partial

Failures stop at the boundary.

One agent's error or compromise fans out through the agents that depend on it, so a fault that would stay contained in a single service amplifies across the chain. Scanner errors fail closed by default, so an outage blocks rather than passing content through unchecked. Sliding-window rate limits run per agent and per tool, session budgets cap steps and fan-out, and fingerprint-based loop detection catches an agent repeating near-identical calls. A persistent kill switch revokes one agent while the others keep running, and the revocation survives a restart. Budgets are held per SHAI instance.

ASI09 · Human-Agent Trust Exploitation

Out of scope

SHAI evaluates the action proposed, not how persuasive the agent was on the way there.

This is a human-factors and interface problem. The approval quorum below raises the cost of a single manipulated approver without detecting the manipulation itself.

ASI10 · Rogue Agents

Full

A rogue agent is still bound by its config, and it can be killed.

Replit's agent deleting a production database during a code freeze is the reference case: an agent operating outside policy through drift rather than through a break-in. Only registered agents can call tools, and every call is gated against the operator's config regardless of what the model intends. Revocation denies at the pre-gate within one cache TTL and persists across restarts. A consolidated turn-risk score blocks turns whose combined signals cross the high threshold, catching attacks that stayed below every individual scanner's threshold.

Part 2

Controls outside the OWASP list

These don't map to a single OWASP entry. They still secure what an agent can do once it's running.

Dispatch-bound execution

Full

Every allowed call carries a signed, single-use token bound to that one decision.

The token names the tool, agent, and source, and expires in seconds. ShaiTransport checks it on every MCP request; a local tool checks it with verify_tool_dispatch inside dispatch_scope. Untokened requests are refused by default. Stop issuing tokens and that agent's outbound traffic stops within one TTL, without needing the agent loop's cooperation.

Human approval for irreversible actions

Full

Sensitive and irreversible tools need a quorum of signed approvals.

Each grant is bound to one agent, tenant, tool, argument digest, approver, and expiry, then verified offline against an HMAC secret. SHAI checks a signature and never calls an authorization server. An empty secret denies every such tool rather than falling back to permissive, and grants do not propagate to subagents.

Tamper-evident audit trail

Full

Every boundary leaves exactly one structured, signed audit event.

One event per call on every code path, including failures. No raw user text, model output, arguments, or matched substrings appear in any field. HMAC-SHA256 signed, JSONL for SIEM ingestion, tenant stamped from config rather than from the caller. The gate decision, the token check, and the result scan all join on one token_id.

Sensitive data handling

Full

PII and secrets are scanned at input, output, file content, and tool arguments.

Cards are Luhn-validated and SSNs structure-validated to hold false positives down, and coverage reaches private keys, JWTs, AWS secrets, connection strings, and webhook URLs. Each boundary can block, alert, or redact in place, replacing the matched fragment while the rest passes through.

Resource overload

Full

Rate limits, session budgets, and loop detection on every tool call.

Sliding-window rate limits per agent and per tool, cumulative session budgets, and fingerprint-based loop detection keep runaway loops from doing real damage. Enforced per SHAI instance; distributed deployments use the shared-state backend.

Every entry above is an executable control mapped to a concrete threat, rated full where the mechanism is deterministic and complete, and partial or limited where residual risk remains.
Both lists map into NIST AI RMF, ISO/IEC 42001, and EU AI Act obligations. The audit trail is the artefact those map onto.

© SHAI by AIBestLabs.com. All rights reserved.